Why we built it
A SIEM is how a security team sees what happens on its network. We wanted to build one end to end: attack a monitored network ourselves, then check that every step left a trace we could find, understand and alert on.
How it works
What we built
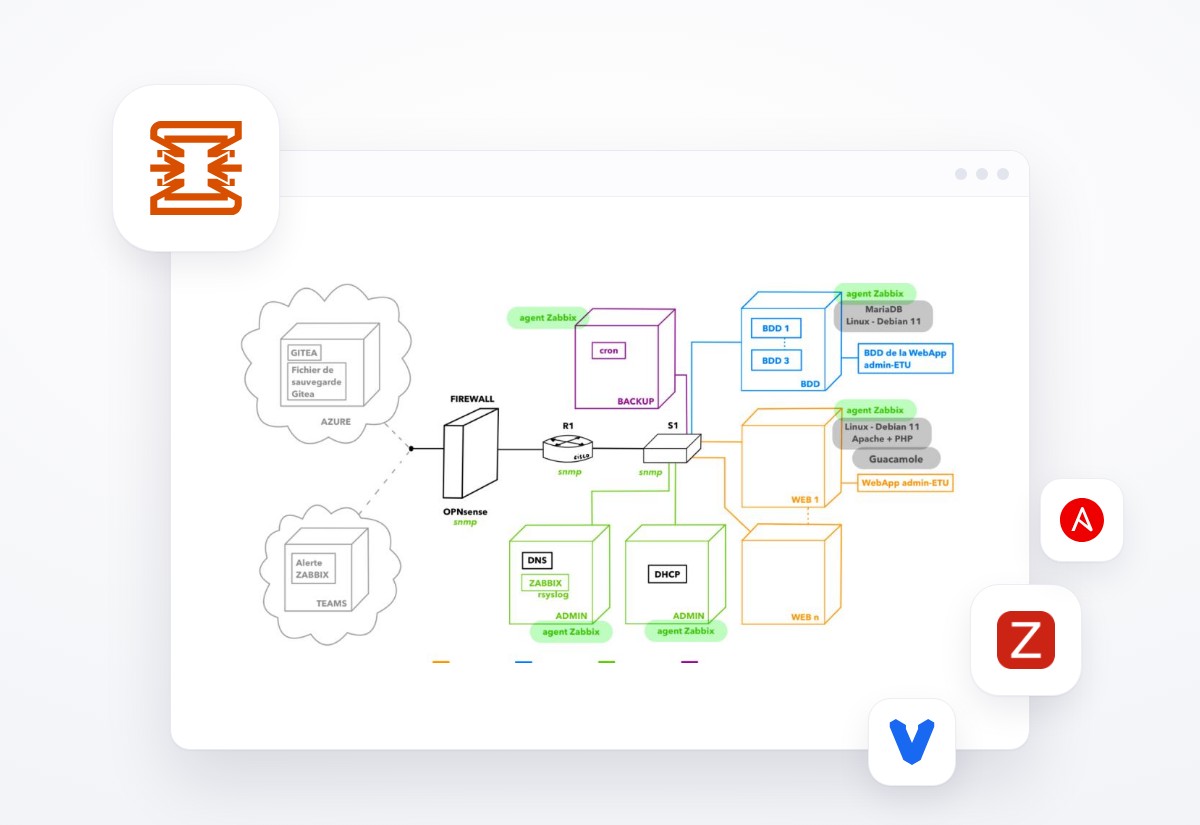
- Built a monitored network of virtual machines, some acting as targets and others as attackers.
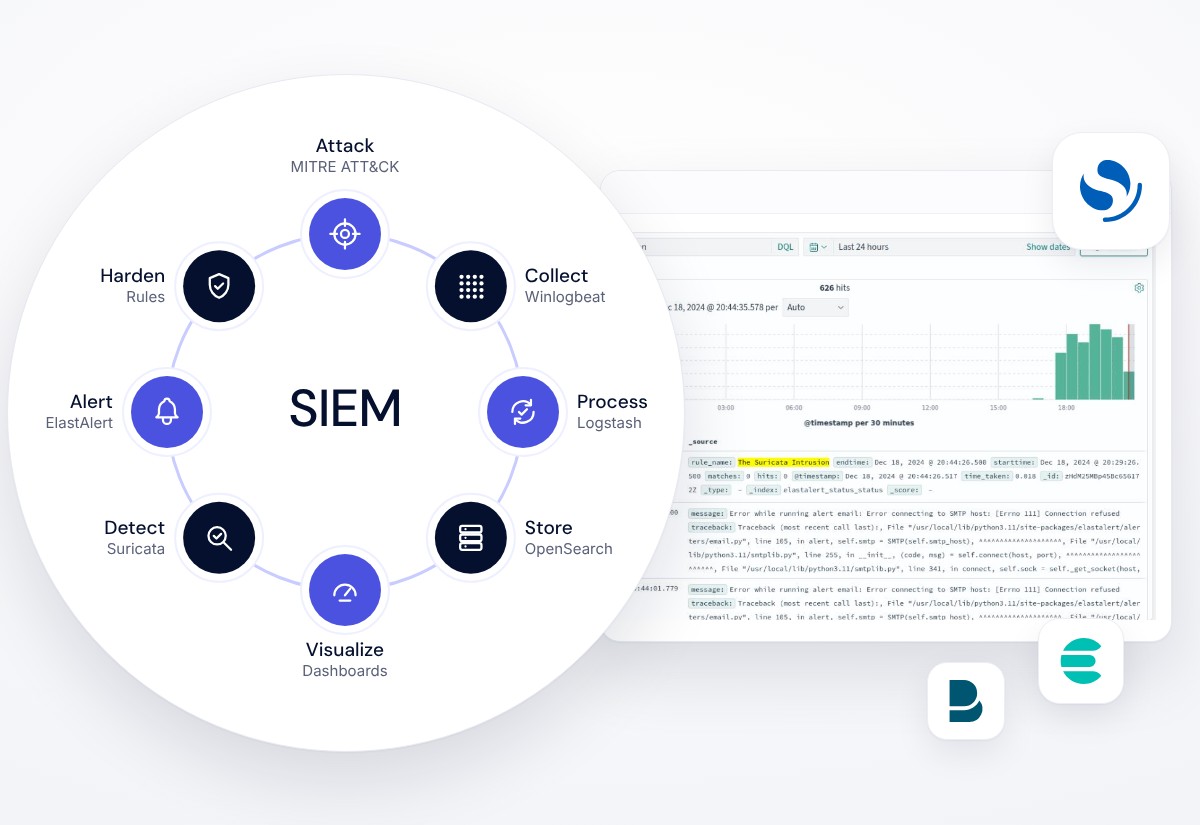
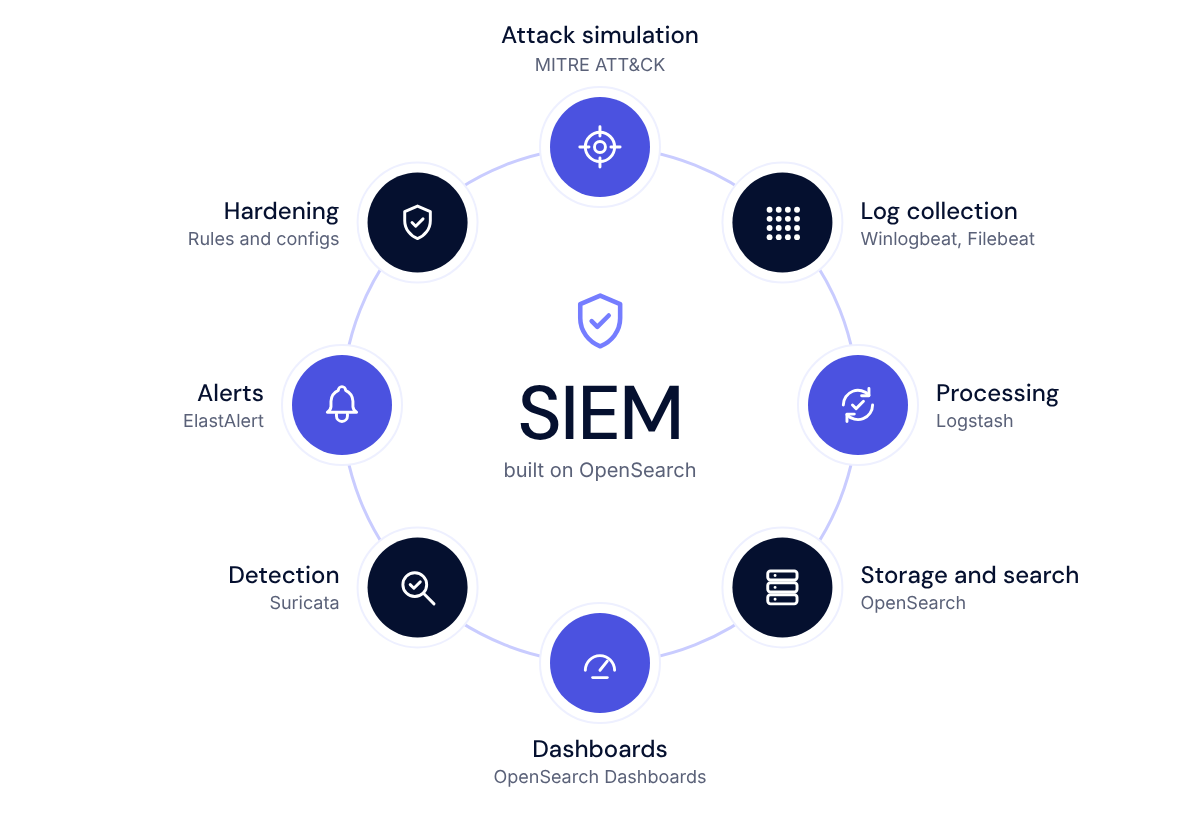
- Simulated attacks such as scans, exploits and malicious files, and mapped each technique to the MITRE ATT&CK framework.
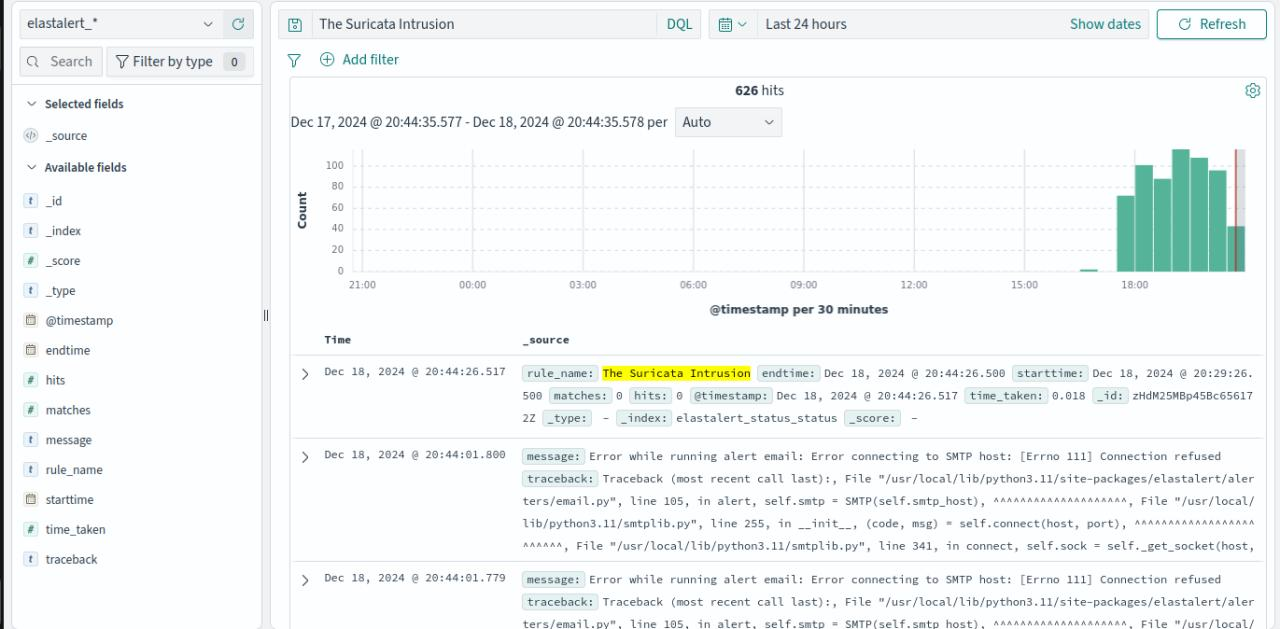
- Collected and centralised logs with Filebeat, Winlogbeat and Logstash into OpenSearch, with OpenSearch Dashboards for visualisation.
- Configured Suricata and ElastAlert to detect incidents and raise alerts in real time.
- Hardened configurations and added security rules to block the attacks we had simulated.
Outcome